article
Zero trust is not a product category
No appliance can sell an organisation the habit of continuously verifying identity, device, context and authority.
Emil Shirokikh · Published September 3, 2026 · Updated September 23, 2026 · 2 min read
Abstract
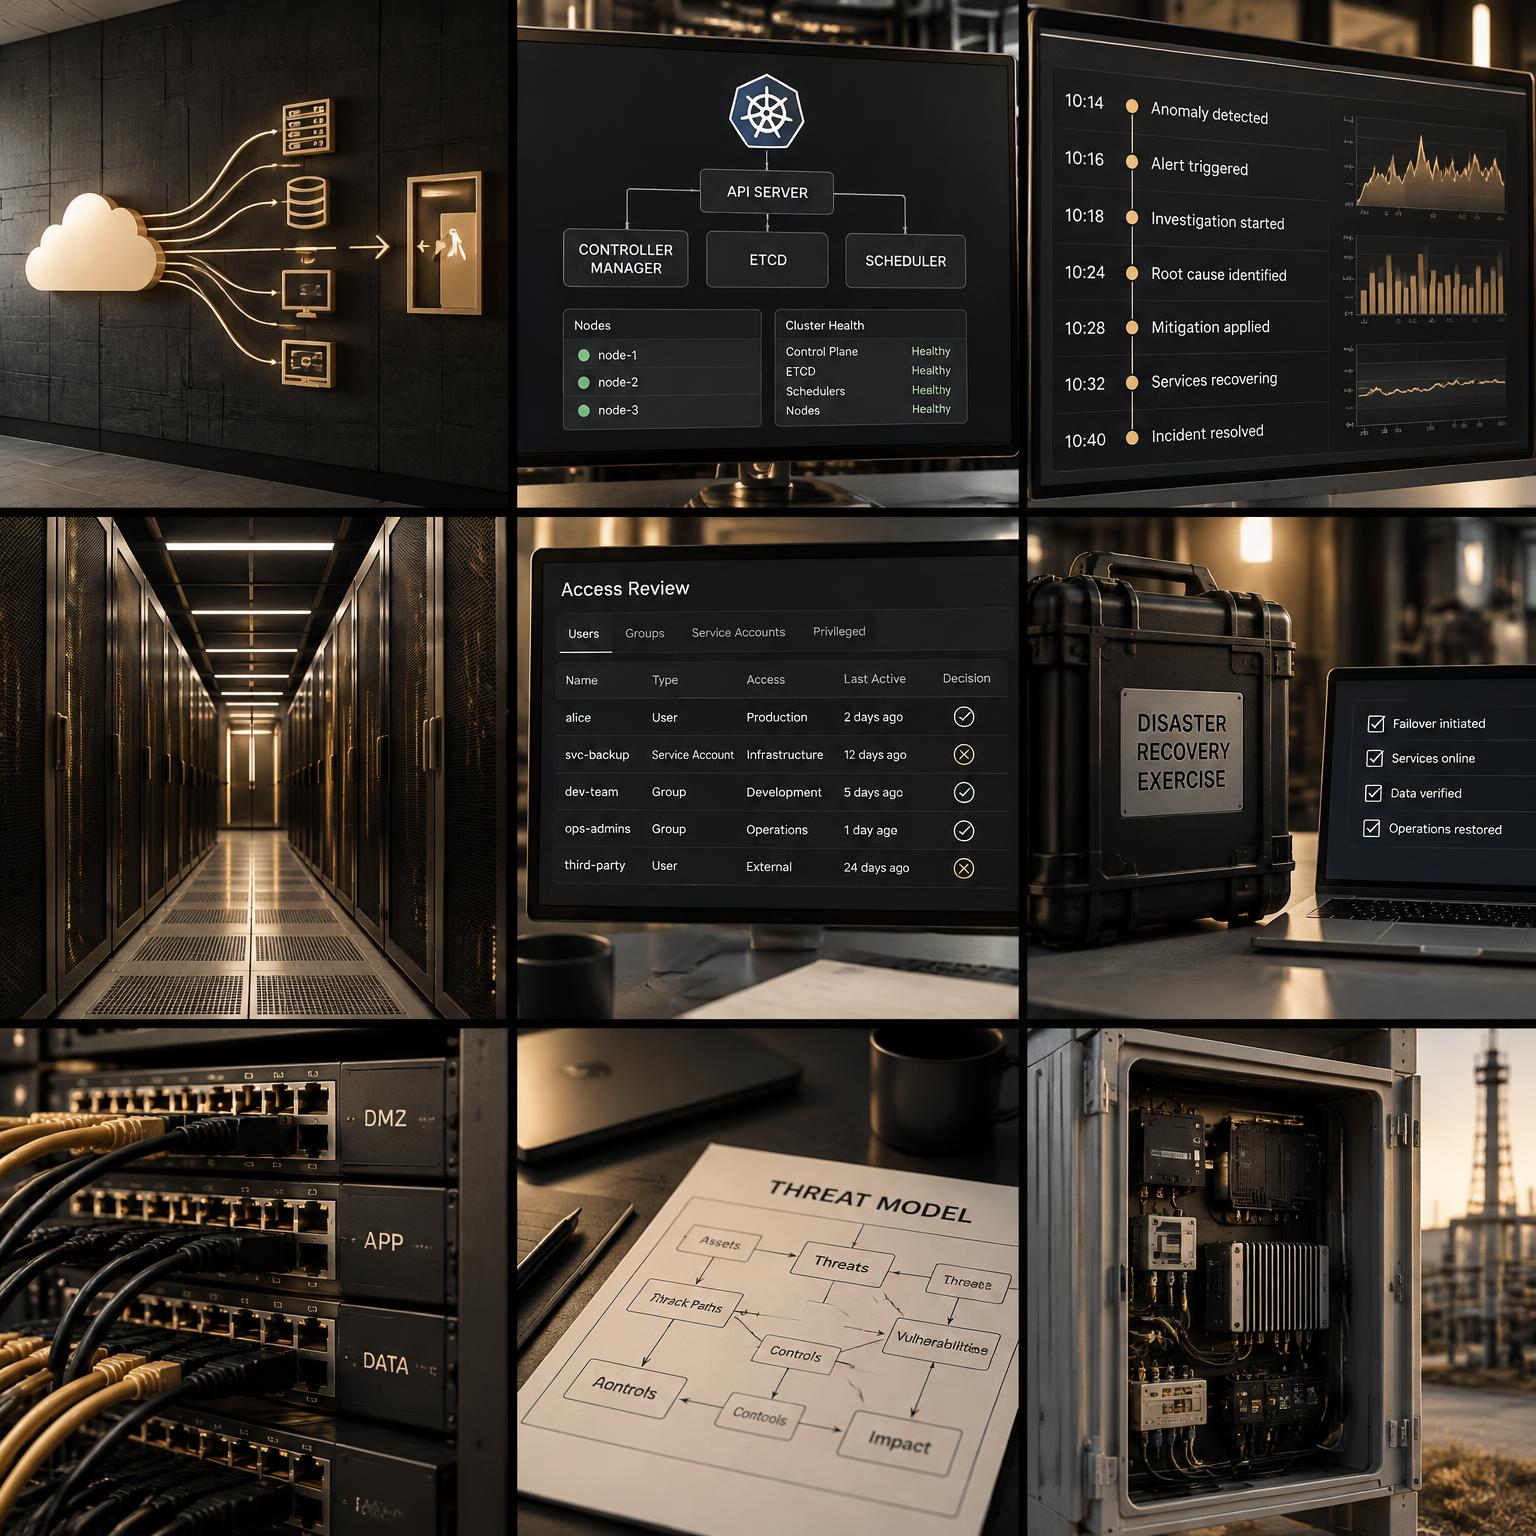
Zero trust is an architectural posture. Product purchases help, but the control emerges from identity quality, segmentation, policy enforcement and observable exceptions.
Design each trust decision
Zero trust emerges from identity quality, device posture, segmentation, policy enforcement and visible exceptions—not from buying an appliance.
Boundary exercise
Select one consequential resource. Trace every identity and service that reaches it, remove standing privilege, define context checks and test denial plus emergency access.
Decision record
Keep a trust-boundary diagram and exception register, then expand resource by resource.
Challenge the conclusion
Platform suites can accelerate adoption. They do not remove the need to design trust boundaries.
Use this in a working session
Attempt access with a stale device, excessive role and unavailable policy service. Record whether denial and recovery are safe.
BELTO editorial analysis. It does not describe a client engagement or claim a commercial result.
References
2 sourcesAuthor
Emil ShirokikhFounder
Founder of Belto Inc. Writes on engineering, venture building and applied intelligence.
Related
Read next
Most AI pilots should be killed sooner
The polite fiction around enterprise AI is that every pilot teaches something. Many teach only that nobody defined the decision, owner or failure cost.
AI agents need boundaries, not personalities
The market is decorating automation with human traits while neglecting permissions, reversibility and evidence.
A computer-vision demo is not a system
Benchmark accuracy says little about glare, drift, maintenance, latency or the operator who must act on an alert.